
Key Takeaways
- The Personal Agent Protocol has moved through 3 drafts in 17 days: 0.1 on 9 October 2026, 0.2 on 24 October 2026, and 0.3 now in progress (changelog).
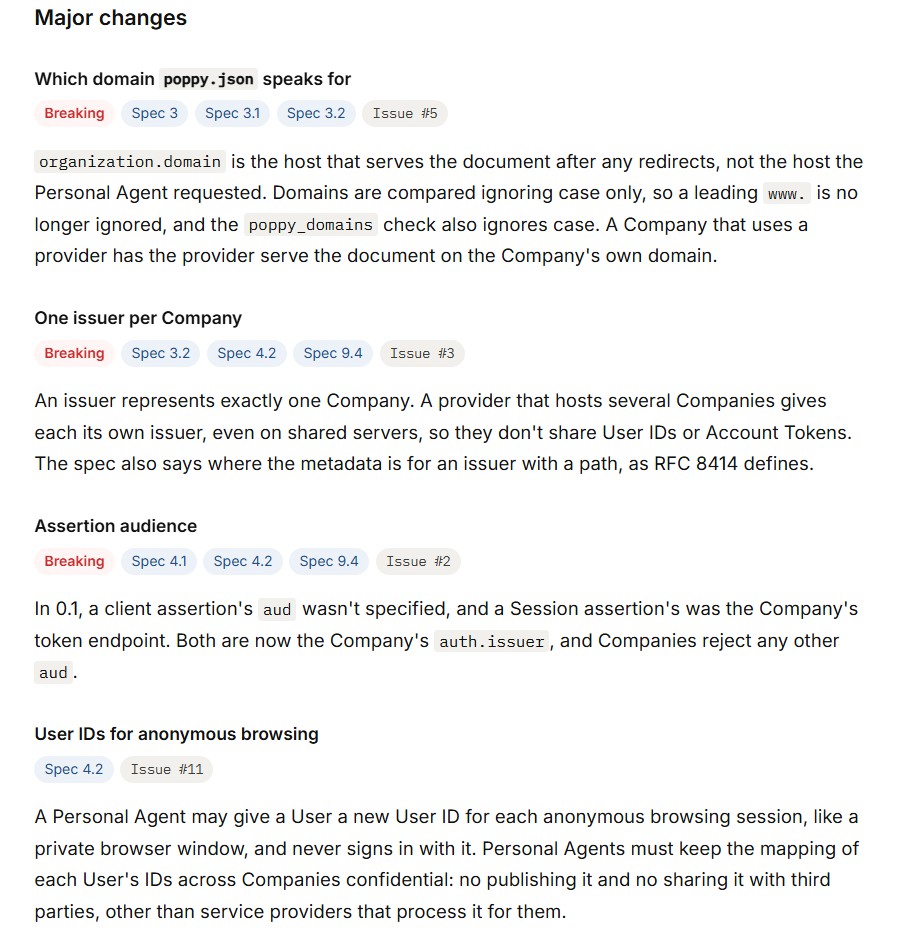
- By our count of that changelog, 39 changes are tagged “Breaking”: 24 in draft 0.2 and 15 so far in draft 0.3.
- 43 design partners are publicly listed, including OpenAI, Visa and Mastercard. Anthropic, Google, Amazon and Apple are not (Path to 1.0).
- The spec admits that off-the-shelf OAuth servers “generally don’t accept” the grant that starts a Session, so every company needs some custom auth work (spec, section 4.2).
- Our verdict: prototype it now, ship to production after version 1.0.
Table of Contents
The short answer
The Personal Agent Protocol is an open standard from Meta and Sierra for AI agents acting for customers. It lets an agent find a business, sign in through OAuth with limited permissions, and finish tasks. It is still a draft (0.3), so prototype it now and ship after version 1.0.
What is the Personal Agent Protocol?
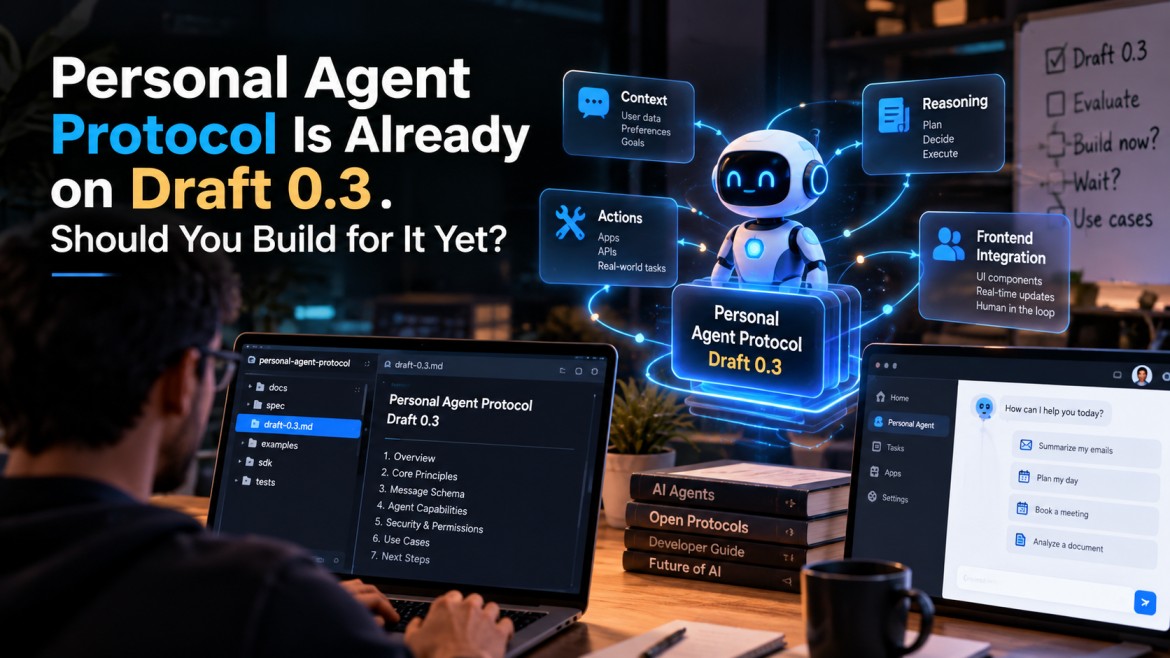
The Personal Agent Protocol, nicknamed Poppy, is a draft open standard for how your AI agent works with a company on your behalf. Meta and Sierra announced it on 6 October 2026 (Unite.AI).
The problem is real. Personal agents today load pages and click through forms like a human. Companies cannot tell a genuine customer’s agent from a scraper, so they block both.
Poppy gives agents a proper front door: one published file, a standard sign-in, and three ways to get work done. The spec is Apache 2.0 licensed and developed in public on GitHub.
How does an agent actually get things done with a company?
In five steps, built almost entirely on existing OAuth standards (spec, draft 0.3):
- Discover. The company publishes a JSON file at /.well-known/poppy.json. It lists the sign-in options, APIs (OpenAPI or MCP), the company’s own agent and its website.
- Start signed out. The agent identifies itself and opens a Session. The company sees an opaque User ID that differs at every company, so companies cannot match users across sites.
- Sign in only when needed. The customer signs in on the company’s own page (Direct), with a link and code (Device), or hands credentials to the agent (Mediated). The spec calls Mediated transitional and plans to remove it.
- Act through one of three doors. The website, the APIs, or a conversation with the company’s agent, which can hand off to a human.
- Sign out. Revoking the long-lived Account Token ends account access. Sessions carry on signed out.
Two security choices stand out. Every token is bound to a per-Session key using DPoP (RFC 9449), so a stolen token is useless on its own. Session assertions must expire within 5 minutes, and Session Tokens should last hours, not days (spec, section 4.2).
Draft 0.3 also forces agents to keep tokens, private keys and sign-in codes out of the model’s context entirely (changelog). That closes an obvious prompt-injection route. It pairs well with the audit-trail argument in our piece on AI incident receipts.
How fast is the spec changing?
Very fast: 39 breaking changes in 17 days, about 2.3 a day. We counted every entry tagged “Breaking” in the official changelog on 26 October 2026.
| Draft | Date | Changes tagged Breaking (our count) | Biggest change |
| 0.3 | In progress (checked 26 Oct 2026) | 15 so far | Company-defined scopes replace poppy:read and poppy:write; browser sign-in redesigned to block session hijacking |
| 0.2 | Published 24 Oct 2026 | 24 | One OAuth issuer per company; backward-compatibility promise deferred to 1.0 |
| 0.1 | Published 9 Oct 2026 | First draft | poppy.json discovery, sessions, sign-in, conversations |
This churn is healthy for a draft. Several changes fix genuine attacks, such as a browser trick that could have signed a victim into an attacker’s account.
But it has a practical cost. Any guide still showing poppy:read and poppy:write scopes is already describing a protocol that no longer exists. The spec itself warns that any part can change before a stable version.
How is Poppy different from MCP, A2A and Visa’s Trusted Agent Protocol?
Poppy covers the customer relationship: who the agent works for and what it may touch in their account. The others cover tools, agent chatter or checkout.
| Protocol | Led by | What it solves | How the agent proves identity | Payments | Status on 26 Oct 2026 |
| Personal Agent Protocol | Meta, Sierra | An agent signs in to a business for one person and acts through web, API or company agent | OAuth with DPoP-bound tokens and an HTTPS client ID | Open topic, not in spec | Draft 0.3 |
| MCP | Open spec, started by Anthropic | Connects an AI app to tools and data | Optional OAuth | No | Dated stable versions |
| A2A | Started by Google | Agents exchanging tasks with other agents | Agent Card at /.well-known/agent-card.json | No | Version 1.0.0 |
| Visa Trusted Agent Protocol | Visa, with Cloudflare | Merchants verify an approved shopping agent at checkout | HTTP Message Signatures (RFC 9421) | Yes, Visa network | Live since 14 Oct 2025 |
Poppy sits above MCP, not against it. A company can list an MCP server as one of its APIs, as long as it runs MCP version 2025-06-18 or later (spec, section 6).
The “rival to Visa” framing in early coverage is overstated. Visa and Mastercard are both listed Poppy design partners (Path to 1.0). The likelier outcome is that payments become a Poppy extension that leans on existing card-network protocols.
If your agent also renders results in a frontend, that is a third layer again. See our explainer on the AG-UI protocol.
Who has signed up, and who is missing?
43 organizations are publicly listed as design partners. Four of the biggest AI platform owners are not among them (Path to 1.0, read 26 Oct 2026).
| Group | Count | Who |
| Companies | 21 | Banking and lending (7), insurance (4), retail (4), media and telecom (4), travel (2), including Walmart, Target, Bank of America, GEICO and United Airlines |
| Technology providers | 19 | Cloudflare, Okta, Shopify, Stripe, Visa, Mastercard, Zendesk, Genesys and others |
| Personal agents | 3 | Meta, OpenAI, Instinct |
The absences matter more than the list. Anthropic, Google, Amazon and Apple are not listed. CNBC reported on 6 October 2026 that Anthropic was not on board, and that Amazon had blocked Meta’s agents (CellCog summary of CNBC).
Be skeptical of the word “partner”. The page lists those who agreed to be named and says the authors are implementing with “several” of them. A community check on 12 October 2026 found no partner serving poppy.json yet (DEV Community).
What does a company actually have to build?
Mostly standard OAuth plumbing, plus one piece almost nobody’s auth server does out of the box. The spec says off-the-shelf servers generally reject the grant that starts a Session, because the user is new to them (spec, section 4.2).
| Component | Standard or custom | What it involves |
| poppy.json file | Standard JSON | Lists your OAuth issuer, scopes, APIs, company agent and web endpoint |
| OAuth server metadata | Standard (RFC 8414) | Must list required grant types and every domain the issuer serves |
| Session start grant | Custom | Accept a signed assertion for a User ID you have never seen; the guides compare 3 approaches |
| DPoP-bound tokens | Standard (RFC 9449), often unsupported | Every API verifies a signed proof per request; ES256 is mandatory |
| Scope descriptions and hints | New fields | Describe each scope; flag changes as none, reversible or irreversible |
| Browser session join | Custom page | One-time code of 128 random bits, expiring within 60 seconds |
| Company agent conversations | Custom, optional | JSON over HTTPS, with streaming and handoff to a person |
| Mediated sign-in | Optional, transitional | Rate limits and one-time codes; scheduled for removal |
We will not invent a person-week estimate. Effort depends almost entirely on whether your authorization server already speaks DPoP and the JWT bearer grant.
The ecosystem is moving anyway. A third-party Python and TypeScript SDK on PyPI already implements draft 0.2, which shows interest and also how quickly code goes stale.
One more parallel is worth noting. Like the much-hyped llms.txt file, a well-known JSON file does nothing until agents actually read it. Our llms.txt test is a useful reminder to wait for real traffic before investing heavily.
Should you implement it now?
Prototype yes, production no, unless you are already a design partner. Version 1.0 has no published date, and a draft can still break your code (Path to 1.0).
| If you are | Do this now | Why |
| A large consumer brand or listed partner | Build against draft 0.3 in staging and file GitHub issues | You can still shape scopes, payments and push notifications before 1.0 |
| An AI agent builder | Build the client side behind a feature flag | Agents must refuse a poppy.json whose version they don’t support, so pin versions strictly |
| A bank, insurer or other regulated firm | Start with scope design and a risk review, not code | Scope hints mark irreversible actions; payments are still an open topic |
| A merchant on Shopify, Stripe or Zendesk | Wait and watch your platform | All three are listed technology partners and may ship support for you |
| A small business with no public API | Do nothing yet | Without APIs or an agent endpoint, agents can only browse you as a signed-out site |
The honest risk of waiting is small. Draft 0.2 already dropped the promise that newer versions won’t break older agents, deferring it to 1.0 (changelog). Early code will need rework either way.
What should you do this week?
Six low-cost steps that stay useful whatever the final spec looks like:
- Audit your OAuth server. Check whether it supports DPoP (RFC 9449) and the JWT bearer grant (RFC 7523). These two decide most of your effort.
- Write your scope list. Name every action an agent might take and label it none, reversible or irreversible. Draft 0.3 asks for exactly this.
- List your excluded tasks. Decide what agents may never do, such as closing an account. Draft 0.3 lets you publish that list.
- Skip Mediated sign-in. It means accepting customer passwords from agents, and the spec plans to remove it.
- Put a staging poppy.json up. Use the example in section 3 of the spec. Do not publish it on production until your issuer metadata matches.
- Watch the changelog weekly. Star the GitHub repo and re-check the changelog before each sprint.
Conclusion
The Personal Agent Protocol solves a real problem: companies cannot tell a customer’s agent from a scraper. Its design is careful, and its partner list is serious.
But 39 breaking changes in 17 days is the clearest signal available. Design your scopes and audit your auth server now. Write production code after 1.0.
FAQ
Is Poppy the same as the Personal Agent Protocol?
Yes. Poppy is the protocol’s official short name, and the discovery file is called poppy.json.
Does the Personal Agent Protocol replace MCP?
No. A company can list an MCP server as one of its APIs. It must run MCP version 2025-06-18 or later (spec, section 6).
Can an agent pay for things through it?
Not yet. Payments are listed as an open topic, alongside push notifications and attachments (Path to 1.0).
Does my agent get my password?
Not with Direct or Device sign-in, where you sign in on the company’s own page. Only Mediated sign-in shares credentials, and the spec plans to remove it.
When will version 1.0 ship?
No date was published as of 26 October 2026. The authors say they will refine the spec through implementations with design partners first.